$BABYDOGE
Fading QuicklySnapshot Window: 2026-08-04 19:30 UTC · ← Back to Crypto Overview
Social Momentum Summary
Total Engagement - Comments: 0, Retweets: 1, Likes: 9, Impressions: 242
Verbatim Community Citations & Social Evidence 1 source posts analyzed
There is currently a major critical bug for multisig in Coldcard even if you use multivendor multisig where the change address in your psbt can be verified as yours but in reality it is not!!! MOVE YOUR FUNDS NO MATTER WHAT! COLDCARD IS GARBAGE @FullyNoded does an excellent
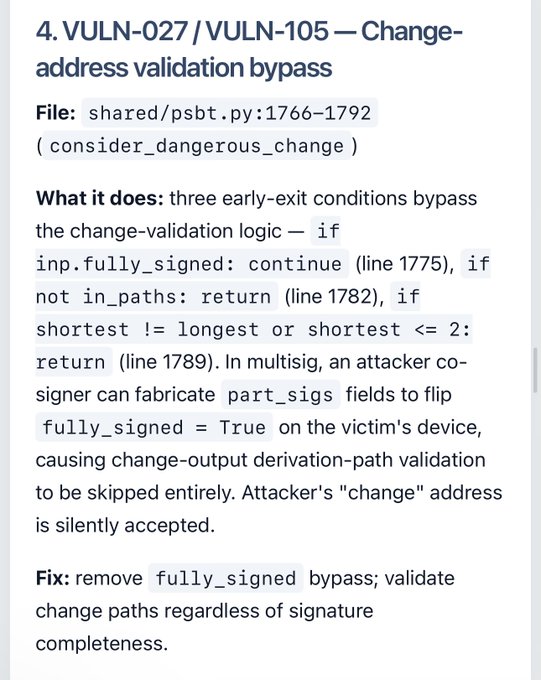
AI visual note: The image shows a technical vulnerability advisory (VULN-027 / VULN-105) for a "Change-address validation bypass" in `shared/psbt.py` lines 1766–1792, detailing how three early-exit conditions (including `if inp.fully_signed`) allow an attacker co-signer to bypass change-validation logic in multisig transactions. This directly supports the post's warning about a critical Coldcard multisig bug where change addresses can falsely appear verified as the user's, making it a legitimate security disclosure that justifies the call to move funds immediately.