$WALRUS Catalyst Posts
June 02, 2026Single-day social intelligence recap and verified catalyst posts · ← Back to $WALRUS Profile · Market Rankings
💬 Curated Viral Posts & Community Evidence
2 source posts analyzed· 2026-06-02T08:12:00+00:00Public blockchains reward transparency AI agents do not Agents managing capital, data, and execution at machine speed do not fit permanently public systems That's where SEAL and @WalrusProtocol step in: > Client-side encryption > Onchain access policies > Decentralized key
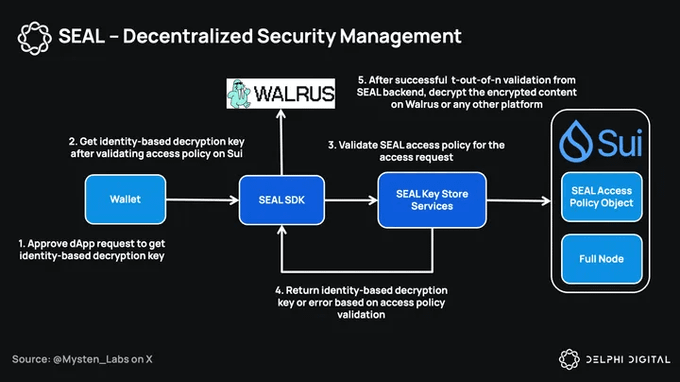
AI visual analysis: The image presents a flowchart that illustrates the process of SEAL decryption using two different systems - Walrus and @WalrusProtocol, as well as Seal Service Policies (SSEP). The post suggests that these protocols should be used for managing client-side encryption at machine speed in order to maintain transparency. It states: 1) Seal does not fit permanently public systems, where neither do any other platforms of @WalrusProtocol or Seal Service policies. That's why SEAL and @WalrusProtocol step in: Client-side encryption. 2) After successful execution from the client side, the server should return an identity-based decryption key (iDK). 3) Validates iDK for the client before sending it to the service via the Seal Store Service. 4) Upon receiving the client's iDK, the client should verify and return the decryption key back to the server through a Signed Value Access Policy. 5) After successful decryption from the server side, the client should then return an identity-based decryption key (iDK). 6) Upon successful completion of this sequence, the client will obtain full mode. 7) Approve request to get. 8) After validation to get, apply decryption.
· 2026-06-02T18:29:27+00:00I am actively staking Walrus; please share your thoughts on this project.