$RLC Catalyst Posts
July 30, 2026Single-day social intelligence recap and verified catalyst posts · ← Back to $RLC Profile · Market Rankings
💬 Curated Viral Posts & Community Evidence
12 source posts analyzed· 2026-07-30T08:00:06+00:00Confidential smart contracts, in Hardhat. Nox now ships with a native @HardhatHQ 3 plugin. One install. Three line config. Your usual test command spins up the whole confidential stack. Same Solidity you already write. Now confidential. docs.noxprotocol.io
AI visual analysis: A promotional graphic featuring a yellow hardhat with the Ethereum logo next to the text 'Nox Protocol', with the tagline 'Run the full Nox stack locally, test end-to-end, right inside Hardhat.' and 'Powered by iExec' at the bottom.
· 2026-07-30T12:32:13+00:00It's going to be a great day !
· 2026-07-30T12:30:03+00:00Every TDX quote contains four RTMR registers. Each attests something different about the running workload. For Nox, one of them does most of the heavy lifting: RTMR3. Here's why it matters
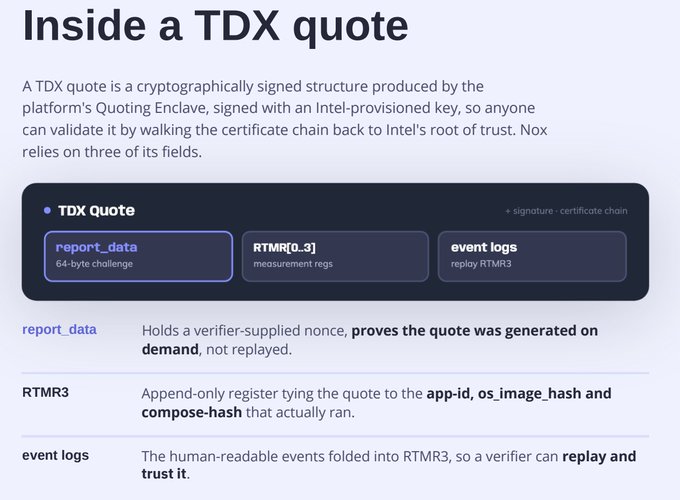
AI visual analysis: A diagram titled "Inside a TDX quote" showing the three key fields—report_data (64-byte challenge), RTMR[0..3] (measurement registers), and event logs (replay RTMR3)—that Nox relies on, with the post emphasizing RTMR3's role in tying the quote to the app-id, os_image_hash, and compose-hash of the running workload.
· 2026-07-30T12:46:49+00:00Super cool ! Even cooler if the USDC were encrypted and private
· 2026-07-30T12:30:07+00:00RTMR0-2 handle boot chain integrity: firmware, kernel, kernel config. RTMR3 records application-specific measurements: app-id, os_image_hash, compose-hash, instance-id, key-provider. These are the fingerprints of the exact code running inside the Trust Domain. Here's how we
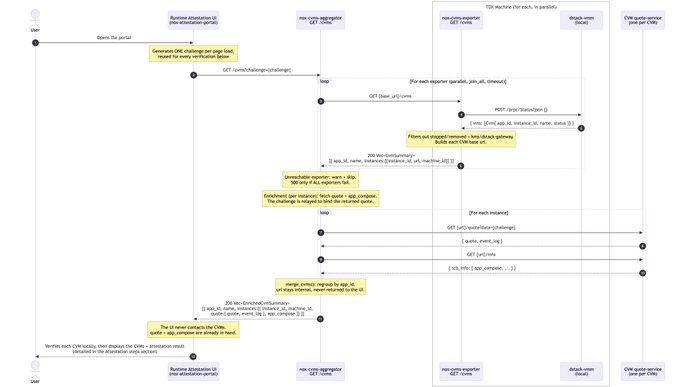
AI visual analysis: A sequence diagram illustrating the attestation process between a User, Runtime Attestation UI (now attestation-perm), a new comp-aggregator (GET /certs), a new comp-supervisor (GET /certs), TDX Machine (drm-stash, tdx-parallel), distroless vmctx (bootd), and CNA quote-service (new per CNA). The diagram shows steps like generating a quote, posting to /dcap, fetching PCR data, retrying on errors, and merging instance IDs, ultimately producing a boot chain integrity verification result that aligns with the description of RTMR0-2 recording firmware, kernel, and kernel config while RTMR3 records application-specific measurements.
· 2026-07-30T12:31:56+00:00@ethereum is for builders. Eth is Home
· 2026-07-30T09:34:19+00:00Privacy that SHOULD work for regulators
· 2026-07-30T12:32:40+00:00Come through to the community hub
· 2026-07-30T09:34:46+00:00Most people don’t realise it untill it’s too late
· 2026-07-30T12:47:58+00:00Thanks for covering us !
· 2026-07-30T09:33:16+00:00Man’s just rotating crashed companies
· 2026-07-30T12:30:10+00:00Why it's the register we focus on: Because verifying RTMR3 is what ties an attestation to a specific Nox component and its docker compose. Boot integrity says the environment is legit. RTMR3 says the workload is Nox. Both are needed. Chain of Trust delivers both.