$E2V
StableSnapshot Window: 2026-09-09 23:40 UTC · ← Back to Crypto Overview
Social Momentum Summary
Total Engagement - Comments: 108, Retweets: 108, Likes: 146, Impressions: 3893
Verbatim Community Citations & Social Evidence 5 source posts analyzed
What happens when builders can create apps where sensitive data does not have to be public? You start opening up markets that were difficult to build on transparent blockchains. Private payments, business tools, trading systems and apps that handle personal data can become more
AI visual note: A stylized graphic with the heading 'The role of encryption in web3' and the word 'SEISMIC' overlaid on a geometric crystal shape against a purple background.
#INX で以前販売していた、 #BCAP がセルフカストディーで取引できる様になりました、っ日本国在住者できるんかぁ#Securitize
A token can be traded. A culture can be worn. Seeing the Flurry rep @lofitheyeti merch IRL is the ultimate proof this is more than an internet moment. We are building a global brand on @SuiNetwork ,one outfit at a time. Real brands outlast cycles. Real chains reward builders Gm
AI visual note: An illustration of a blue monkey character wearing a dark hoodie and cap, both branded with "LOFi," taking a mirror selfie with a smartphone at a desk with a cup of pens.
BREAKING: Trezor’s email provider has been breached. Customers are receiving a non-spoofed email, it’s real, just not sent by the real company. This follows shortly after the breach of their logistics provider, which left 80k+ customers’ data exposed.
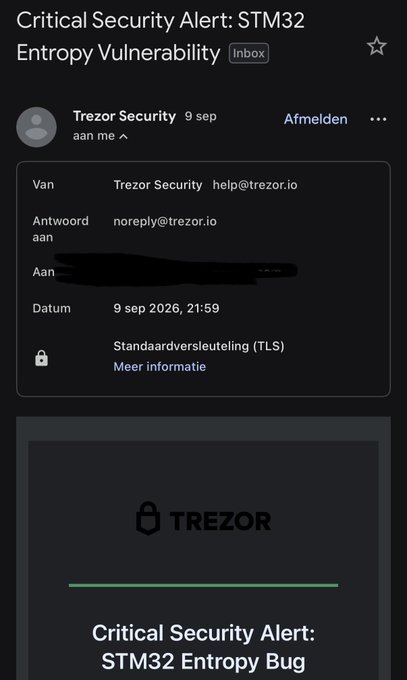
AI visual note: A Gmail inbox displays an email from "Trezor Security" ([email protected]) with the subject "Critical Security Alert: STM32 Entropy Vulnerability," dated 9 sep 2026. The post warns that this email is authentic (not spoofed) but was sent through a breached email provider rather than by Trezor itself, following a recent logistics breach that exposed 80k+ customers' data.
Robinhood chain just got so ugly in the last 6 hours, i have now blasted something on Monad.