$GPRO
Cooling DownSnapshot Window: 2026-09-08 17:30 UTC · ← Back to Crypto Overview
Social Momentum Summary
Total Engagement - Comments: 2, Retweets: 0, Likes: 7, Impressions: 486
Verbatim Community Citations & Social Evidence 1 source posts analyzed
Ok so in trying to fix the first bug, Blockstream introduced a new bug - essentially making it even easier to fake "proof" of a transaction... with a diff amount. This was a deep encryption attack. Now I wonder if they fixed the bug by hand (or with AI) and if they reviewed
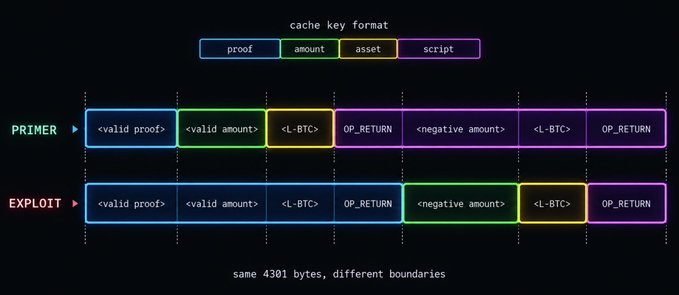
AI visual note: The image illustrates a cache key collision vulnerability in Bitcoin's script verification, showing how the same 4301-byte input can be parsed with different boundaries in the "PRIMER" versus "EXPLOIT" cases—where elements like `<valid proof>`, `<valid amount>`, `<L-BTC>`, `OP_RETURN`, and `<negative amount>` are rearranged—causing the cache to match a legitimate-looking proof to a transaction with a different (negative) amount, thus enabling a deep encryption bypass.