$RLUSD
Cooling DownSnapshot Window: 2026-09-03 04:00 UTC · ← Back to Crypto Overview
Social Momentum Summary
Total Engagement - Comments: 0, Retweets: 0, Likes: 3, Impressions: 2006
Verbatim Community Citations & Social Evidence 1 source posts analyzed
🚨 CrowdStrike and U.S. federal law enforcement have taken down the Russia based Sality botnet, which targeted crypto users by hijacking wallet addresses. Sality monitored the clipboard on infected computers and replaced copied Bitcoin and Ethereum wallet addresses with
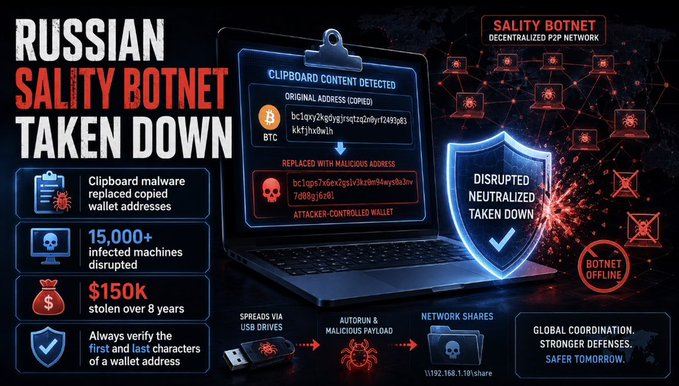
AI visual note: The graphic announces the takedown of the Russian "Sality Botnet," a decentralized P2P network that infected over 15,000 machines to steal $150k over 8 years by replacing copied Bitcoin and Ethereum wallet addresses via clipboard malware—visually illustrating how the attacker-controlled wallet replaced legitimate addresses, leading to its disruption.