$OP_CAT
Fading QuicklySnapshot Window: 2026-08-15 23:10 UTC · ← Back to Crypto Overview
Social Momentum Summary
Total Engagement - Comments: 0, Retweets: 0, Likes: 0, Impressions: 2
Verbatim Community Citations & Social Evidence 1 source posts analyzed
Google has published a paper that might end the entire crypto era. And it is so dangerous they are refusing to publish the code. Every major blockchain, including Bitcoin and Ethereum, relies on an encryption standard called the 256-bit Elliptic Curve. Breaking that encryption
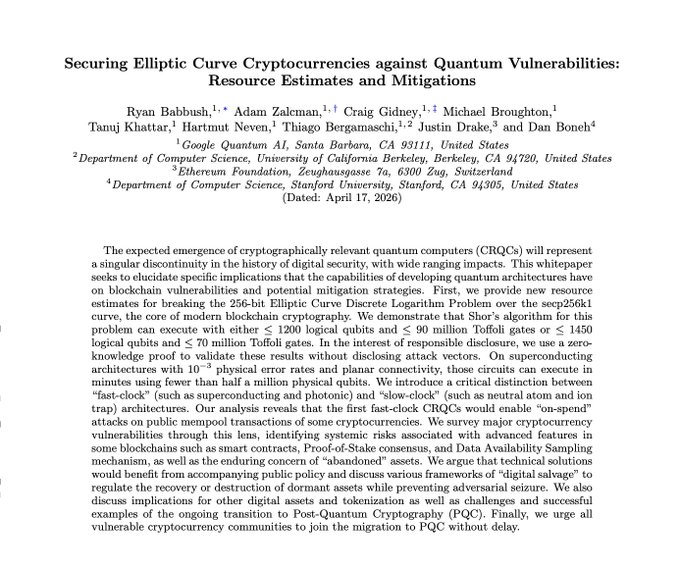
AI visual note: The image shows the title page of a Google Quantum AI research paper titled "Securing Elliptic Curve Cryptocurrencies against Quantum Vulnerabilities: Resource Estimates and Mitigations," co-authored with researchers from UC Berkeley, the Ethereum Foundation, and Stanford University, dated April 17, 2026. The abstract reveals that Google's quantum computers could break the 256-bit Elliptic Curve cryptography underlying most cryptocurrencies—using fewer than 1 million noisy qubits and under 1,450 logical qubits in minutes—while noting that the first fast-clock CRQCs could enable "on-spend" attacks on mempool transactions, supporting the accompanying post's claim about the paper's dangerous implications for Bitcoin, Ethereum, and the entire crypto ecosystem.