$SUI
StableSnapshot Window: 2026-08-14 21:20 UTC · ← Back to Crypto Overview
Social Momentum Summary
Total Engagement - Comments: 4, Retweets: 6, Likes: 40, Impressions: 1065
Verbatim Community Citations & Social Evidence 3 source posts analyzed
By the time they regulate memecoins, retail will already be destroyed.

Dinosaurs on Solana
AI visual note: A pixel art image shows three brown coffin-shaped objects stacked on dark ground.
WASABI WALLET HAD HIGH-SEVERITY OS COMMAND INJECTION VULNERABILITY FOR TWO YEARS A vulnerability introduced in February 2024 could allow an attacker to craft a malicious coordinator link that, if copied into a user’s clipboard and followed by clicking “Read More” in Wasabi,
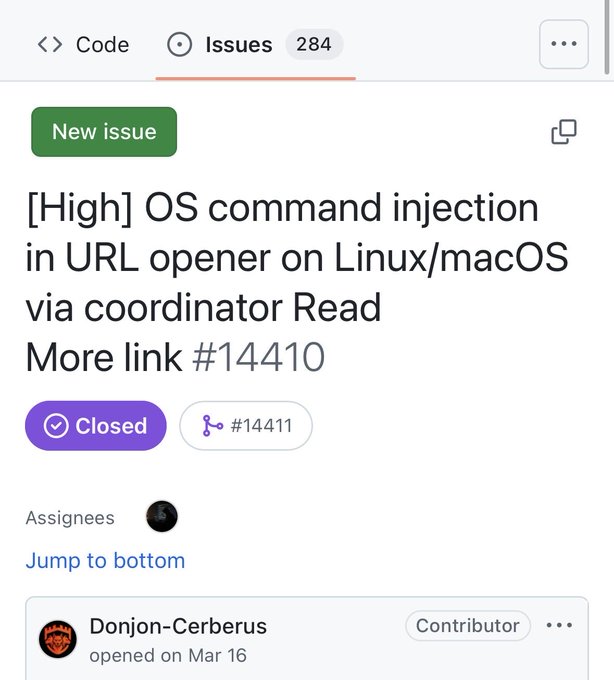
AI visual note: The image shows a GitHub issue page titled "[High] OS command injection in URL opener on Linux/macOS via coordinator Read More link #14410," marked as Closed and linked to issue #14411, filed by contributor Donjon-Cerberus on March 16. The image directly relates to the post by illustrating the high-severity command injection vulnerability reported in Wasabi Wallet's GitHub repository, which could be exploited via a malicious coordinator "Read More" link.