$YEET
Heating UpSnapshot Window: 2026-08-12 21:10 UTC · ← Back to Crypto Overview
Social Momentum Summary
Total Engagement - Comments: 14, Retweets: 19, Likes: 32, Impressions: 600
Verbatim Community Citations & Social Evidence 1 source posts analyzed
Bitcoin developers are flipping the script. LLMs have been used to find vulnerabilities in Bitcoin code. Now @n1ckler is using them to mathematically prove code is secure. His new proof-of-concept library implements the one-time signature scheme at the core of SHRINCS, a
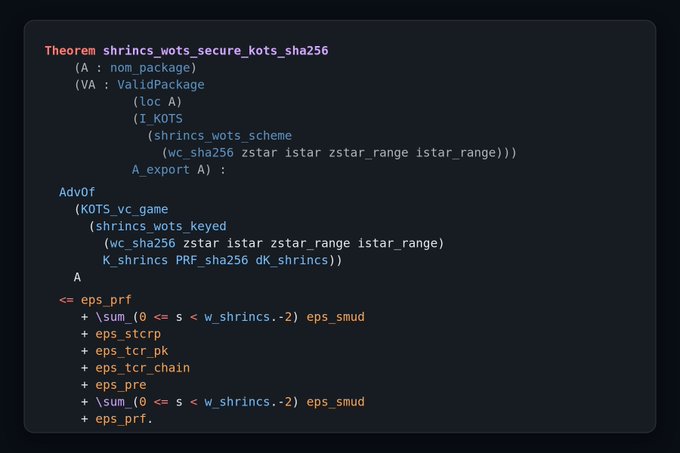
AI visual note: The image displays a Coq formal verification theorem proving the security of the "shrincs_wots" Winternitz one-time signature scheme using SHA-256 against a KOTS (keyed one-time signature) adversary, with an advantage bound combining various epsilon terms (smud, strcrp, tcr_pk, tcr_chain, pre, prf). This relates to the post as it shows Nickler's mathematical proof-of-concept library that uses LLMs to formally verify Bitcoin's cryptography, specifically demonstrating the WOTS scheme at the core of the post-quantum signature scheme SLH-DSA (formerly SPHINCS+/SHRINCS).