$NEAR
Cooling DownSnapshot Window: 2026-08-04 23:20 UTC · ← Back to Crypto Overview
Social Momentum Summary
Total Engagement - Comments: 0, Retweets: 0, Likes: 0, Impressions: 180
Verbatim Community Citations & Social Evidence 1 source posts analyzed
Looks like Coldcard was a state-backed, inside job spanning multiple years of careful planning. The revelation of earlier tweets like the one below heavily suggests that this was long premediated by Coldcard insiders. The heist was optimized around max public shock value and
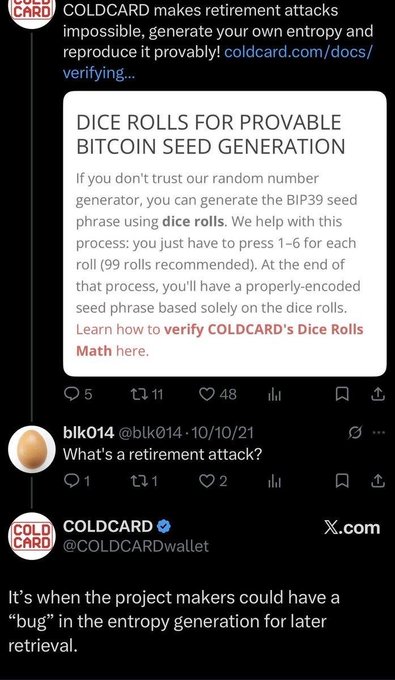
AI visual note: The image shows a tweet from COLDCARD (@COLDCARDwallet) explaining how their device generates entropy using dice rolls to prevent "retirement attacks," followed by a user question and Coldcard's reply defining a retirement attack as when project makers could embed a bug in entropy generation for later retrieval. The accompanying post sarcastically suggests Coldcard's emphasis on "retirement attacks" reveals the company was planning a long-term inside job, framing their transparency about entropy vulnerabilities as evidence of premeditation.