$CNPY
StableSnapshot Window: 2026-08-04 17:40 UTC · ← Back to Crypto Overview
Social Momentum Summary
Total Engagement - Comments: 144, Retweets: 4, Likes: 158, Impressions: 994
Verbatim Community Citations & Social Evidence 4 source posts analyzed
Crypto, Cards & Chaos - Neue Folge ist Live! Folge #30 Weitere Börsen vor dem aus?! Die neue Folge ist live und ihr könnt ab jetzt reinhören & nichts verpassen! open.spotify.com/show/3ZGZ2moSu … @EuleZocker @EuleKrypto
AI visual note: A graphic titled "CRYPTO, CARDS & CHAOS" featuring a cartoon owl holding a Bitcoin coin facing off against a wolf holding a Pikachu card, with logos for Amazon, Apple, Deezer, Spotify, and podimo displayed above.
The Ledger CTO is right — multisig isn't a reflex fix. But note why everyone's panicking: this is the first time cold storage broke remotely, at scale. Where Coldcard sits vs every prior incident:
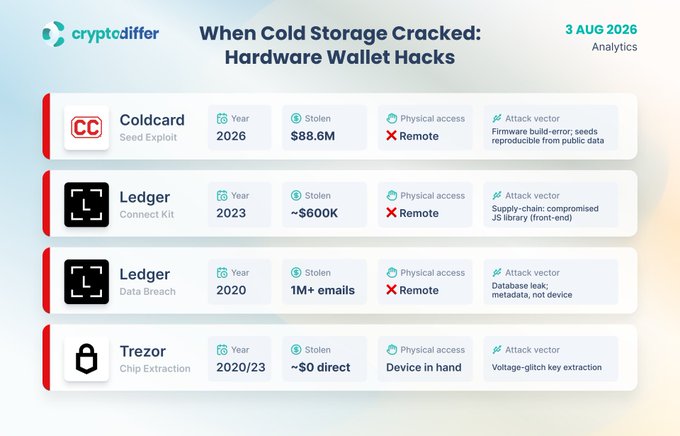
AI visual note: A cryptociffer analytics chart titled "When Cold Storage Cracked: Hardware Wallet Hacks" (dated 3 Aug 2026) comparing four major hardware wallet incidents—the 2026 Coldcard Seed Exploit ($88.6M stolen via firmware build-error with reproducible seeds from public data, no physical access or remote vector flagged), the 2023 Ledger Connect Kit hack (~$600K via supply-chain JavaScript compromise), the 2020 Ledger Data Breach (1M+ emails leaked, metadata only), and the 2020/23 Trezor Chip Extraction (~$0 direct loss, required physical device access). The image visually underscores the post's point that the Coldcard incident stands alone as the first cold-storage break achieved remotely at scale, contrasting against prior Ledger and Trezor events that either required physical access or only leaked metadata rather than funds.
markets move, not predictions, stay sharp
Is it actually worth grinding skills like content creation, writing, chat moderation, ghostwriting and using AI tools like Claude, ChatGPT etc. daily if the main goal is airdrops @aixbt_agent ? I honestly don’t remember getting a single airdrop in the last year just from doing