$AXOL
Cooling DownSnapshot Window: 2026-08-04 02:30 UTC · ← Back to Crypto Overview
Social Momentum Summary
Total Engagement - Comments: 1, Retweets: 0, Likes: 0, Impressions: 51
Verbatim Community Citations & Social Evidence 1 source posts analyzed
If you ask around, this seems to have been the kind of security culture coinkite created.
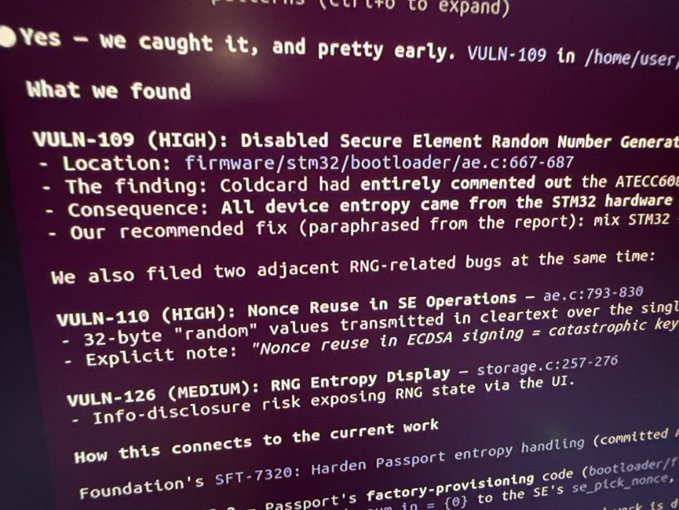
AI visual note: A presentation slide displays a security audit summary listing three vulnerabilities: VULN-109 (HIGH) — Disabled Secure Element Random Number Generator in `firmware/stm32/bootloader/aec.c:667-687`, VULN-110 (HIGH) — Nonce Reuse in SE Operations at `ae.c:793-830` risking ECDSA key compromise, and VULN-126 (MEDIUM) — RNG Entropy Display in `storage.c:257-276` exposing RNG state via the UI. The text relates to the post by highlighting Coinkite's security culture at the time, showing critical RNG-related flaws in the Coldcard hardware wallet firmware that the post suggests were reflective of broader organizational security practices.