$DOGE
Fading QuicklySnapshot Window: 2026-08-01 00:20 UTC · ← Back to Crypto Overview
Social Momentum Summary
Total Engagement - Comments: 11, Retweets: 1, Likes: 20, Impressions: 2768
Verbatim Community Citations & Social Evidence 2 source posts analyzed
How can you tell a seed generator has 256 bits of entropy if you don't check all 115,792,089,237,316,195,423,570,985,008,687,907,853,269,984,665,640,564,039,457,584,007,913,129,639,936 keys? Obviously you can't generate that many keys to check and if you could then they wouldn't be secure. I'm asking if there is a test to determine if a method does actually have the necessary randomization to achieve that many possible different combinations. For example could someone have generated keys using a flawed ColdCard at a very high rate, then simply have checked if it made any duplicates? If the entropy was so low that a laptop can crack them, this method surely would have immediately revealed an issue. Meanwhile my HWW manufacturer put out a statement that their devices have always had the full 128 or 256 bits and there's nothing to worry about. Not feeling especially secure though.
Another day another exploit This time Hardware @COLDCARDwallet Total loss - 584 $BTC $38M On Bitcoin Here is the story A firmware bug introduced 5 years ago caused some Coldcard devices to generate wallet seeds with much lower randomness than intended Easy
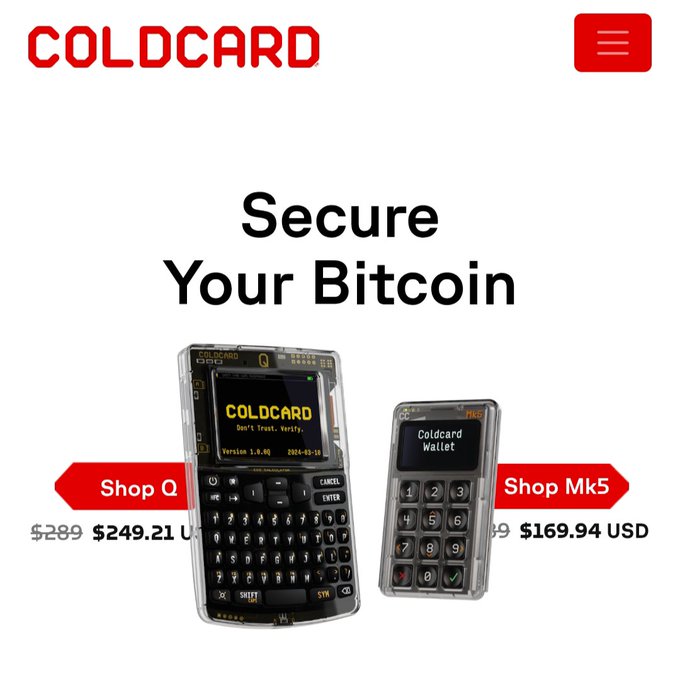
AI visual note: The COLDCARD website homepage advertises its Bitcoin hardware wallets with the tagline "Secure Your Bitcoin," featuring the Q model at $249.21 USD and Mk5 at $169.94 USD. The image ironically contrasts with the post's claim about a firmware vulnerability that caused reduced randomness in wallet seed generation on some devices.