$BTC
StableSnapshot Window: 2026-09-30 12:10 UTC · ← Back to Crypto Overview
Social Momentum Summary
Total Engagement - Comments: 66, Retweets: 23, Likes: 201, Impressions: 23828
Verbatim Community Citations & Social Evidence 34 source posts analyzed
this is what happens when you get so underwater on a short that you start praying to god
This time, besides joining a few deals on the B Vàng exchange, I'm also joining the deal from @bitget , okay. Today, I'm introducing the Bitget Alliance Program (from 15:00 on 28/09 to 15:00 on 26/10, VN time): Reward pool equivalent to 30% of the platform's actual net
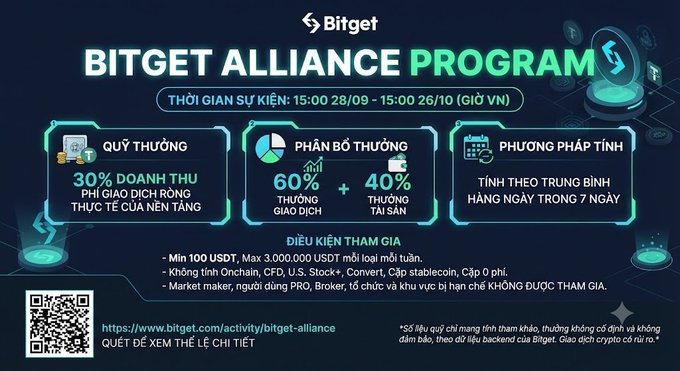
AI visual note: The image is a promotional banner for the **Bitget Alliance Program**, running from 15:00 on 28/09 to 15:00 on 26/10 (Vietnam time), highlighting a 30% revenue reward pool split into a 60% trading rebate and 40% asset rebate, with eligibility requiring a minimum of 100 USDT and up to 3,000,000 USDT in weekly trading volume across spot and futures markets.
You have to wait years and years to be in the same cycle-situation like we are now for ALTs Dont miss pls
$TIA taught me that there is a position between holding and selling. It is called waiting for one more reason. Every time I was ready to leave, I found one. Another update. Another argument. Another maybe. @lubobtetrevass watched the exit plan slowly become a
NEW STATE STREET LIQUIDITY FUND IS NOW LIVE ON THE STELLAR NETWORK “Stellar has run in production for more than a decade at 99.99% uptime, and SWEEP now puts one of the world's largest money market fund issuers on the Stellar network.” Documented below.
AI visual note: A screenshot from the Stellar website announces "State Street Galaxy Onchain Liquidity Sweep Fund Goes Live on Stellar," published September 29, 2026 at 8.00 AM EST, featuring the Stellar logo on a yellow banner that corresponds with the post's announcement of the new State Street liquidity fund launching on the Stellar network.
"I think this likely ends up being our cycle bottom accumulation range." 4 months later. Hope y'all printing with me and didn't fall for the bear propaganda.
JUST IN: U.S. spot Bitcoin ETFs have recorded pulled in roughly $3.1 BILLION over 9 straight sessions. $ETH ETFs flipped negative, shedding nearly $3M as institutional demand concentrates more heavily on $BTC .
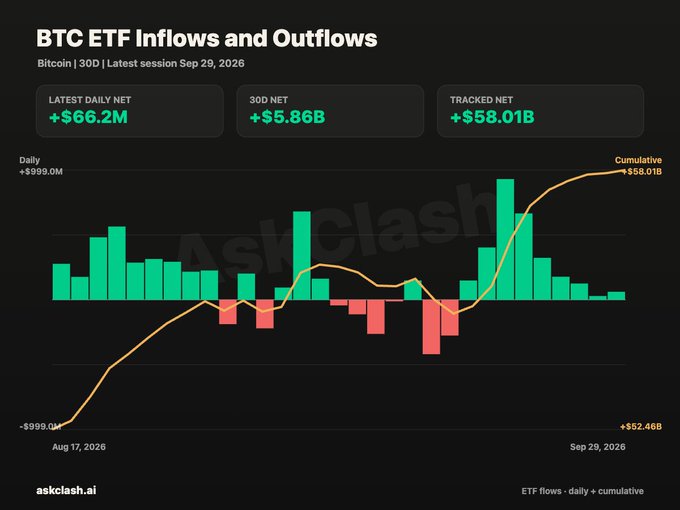
AI visual note: A dashboard titled "BTC ETF Inflows and Outflows" from AskClash shows Bitcoin ETF data with $66.2M latest daily net inflows, $5.86B 30-day net, and $58.01B tracked net, visualized through green and red daily bars alongside an orange cumulative line chart spanning August 17 to September 29, 2026—corroborating the post's claim of sustained Bitcoin ETF inflows totaling roughly $3.1B over nine straight sessions.
Neymar’s first season at PSG was a different level
Wishing you a blessed and bountiful day Good morning
TOKEN2049 Singapore, DeJob is giving everyone some perks! This time, teaming up with @uxuyzh , we've prepared 4 shares of 【Free Health Check Benefits】 for the DeJob community—drawing 4 lucky friends, one share each! Participation is super simple: ① Follow @DeJob_Official
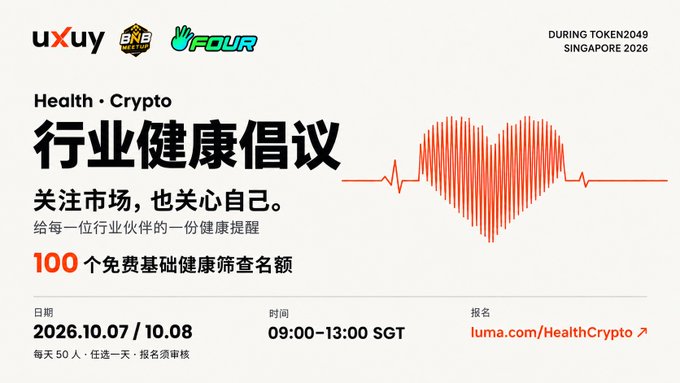
On a personal note, I have left Finanche Co., Ltd. Since joining the company, I was entrusted with responsibilities in the marketing domain. Starting in October, I will embark on a new challenge in the AI domain. To everyone who took care of me during my time there, thank you
I keep finding more games every time I go through @PlayOnMint casino This time I checked the Featured section and found: RUSH HOUR ROLLING DUNES CRAZY TIME CHAOS CREW MONSTER BLOX GOOD GIRL BAD GIRL I’ve already seen a few of these in other sections, but Monster Blox and Good
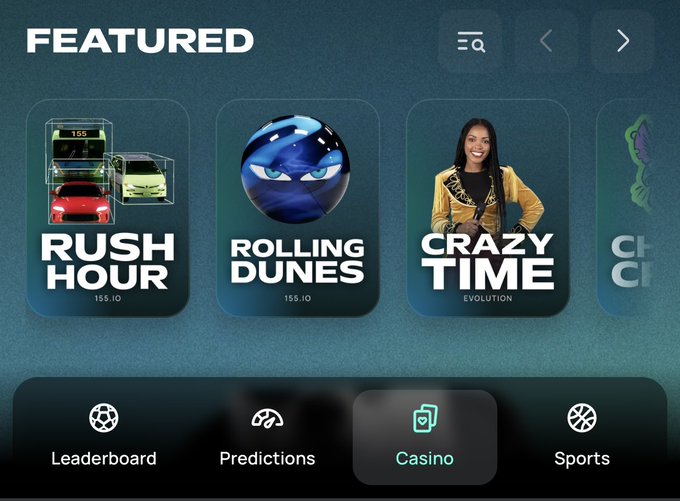
AI visual note: A digital interface displays a 'FEATURED' section with game tiles including 'RUSH HOUR,' 'ROLLING DUNES,' and 'CRAZY TIME,' with a bottom navigation menu showing options for 'Leaderboard,' 'Predictions,' 'Casino,' and 'Sports.'
Token2049 is in 7 days wow kinda nervous, so much is going down but also lots of fun and many friends to catch up with
Robinhood is Winning, Abstract is .. What is going on? Coffee with Captain #1,259
DELIVER! DELIVERANCE! DELIVER THE MOON, MARS, SATURN!!! DELIVER 589!!! XRP $589
i genuinely think $hype will see $100 soon. the more i watch hyperliquid grow, the more the thesis makes sense to me. volume, revenue, hyperevm, buybacks. it’s becoming way bigger than just a trading chain. if i’m buying anything again, i’ll probably keep stacking more $hype .
BREAKING: STANDARD CHARTERED SEES ETHENA'S USDe GROWING ROUGHLY 8X IN TWO YEARS Standard Chartered sees potential for USDe to grow about 8x over the next two years as DeFi and TradFi converge. $ENA
Is it real $QUBIC ?
Leaks, news, and updates! Don't miss the Mokiside chat happening today! Join @Moku_HQ 's Discord for more
Want to connect with other people building, using, and experimenting with BSV? We have a public BSV community on Telegram where you can ask questions, share what you’re working on, discuss ideas or BSV posts, help others, or simply follow along with what’s happening across the
Good morning Degens
AI visual note: Two men in suits stand together in a casino setting, one holding a cigarette.
DARKSWORD EXODUS I have been digging into the recent iOS exploit research because I think it is particularly relevant to people using self-custody wallets such as Exodus on an iPhone. There is a lot of sensational information circulating, so it is important to separate what researchers have actually demonstrated from what is still speculation. The strongest documented case is DarkSword, a full iOS exploit chain investigated by Google Threat Intelligence Group, Lookout and iVerify. Google says the chain was being used in the wild from at least November 2025 by multiple threat actors, including commercial surveillance vendors and suspected state-sponsored operators. The confirmed target range was iOS 18.4 through iOS 18.7. What makes DarkSword important for an Exodus user is that this was not a normal phishing attack where somebody simply asks you to type your recovery phrase into a fake website. The attack could begin with the victim visiting a malicious or compromised webpage. From there, the chain exploited several different layers of iOS until the attacker could reach extremely privileged areas of the device. Technically, the chain was essentially this Google reconstructed six vulnerabilities involved in DarkSword. CVE-2025-31277 and CVE-2025-43529 attacked JavaScriptCore depending on the iOS version. CVE-2026-20700 was used in the process of defeating Pointer Authentication. CVE-2025-14174 provided another stage of sandbox escape through ANGLE and WebGL. CVE-2025-43510 exploited XNU to move into a more privileged process. CVE-2025-43520 ultimately provided powerful kernel memory capabilities. That distinction matters enormously. Breaking Safari alone does not mean that somebody owns your iPhone. Modern iOS security is built like several vault doors behind one another. WebKit is one door, PAC is another, the sandbox is another and the kernel is another. A full exploit chain works because the attacker finds a different key for each door. DarkSword was dangerous precisely because researchers found evidence of that entire chain being assembled and deployed. After successful exploitation, Google identified three malware families associated with the operation called GHOSTBLADE, GHOSTKNIFE and GHOSTSABER. Lookout described DarkSword as capable of rapidly extracting sensitive information including credentials and cryptocurrency wallet data before attempting to remove evidence of its presence. This is where . Exodus is a self-custody wallet. Exodus does not hold your private keys on its servers. The private keys are generated and encrypted locally and stored on your device. The Exodus 12-word secret key is effectively the master secret from which the wallet derives its private keys. Whoever obtains that secret can ultimately control the corresponding funds. That architecture protects users from an entirely different class of risk. Compromising Exodus servers does not simply give an attacker everyone’s private keys because Exodus does not possess them. But self-custody also moves the security boundary toward the endpoint. That is why an iOS kernel exploit deserves far more attention from a crypto holder than an ordinary Safari bug. It is also important not to exaggerate what the DarkSword research proves. Lookout explicitly reports exfiltration involving cryptocurrency wallets, but the currently public research does establish that DarkSword universally extracted the Exodus 12-word secret key from every compromised iPhone. Saying that would go beyond the evidence currently available. There is an important difference between and Those are not interchangeable claims. Exodus itself states that its 12-word secret key is encrypted and stored on the device and that the company does not store or have access to it. Exodus also warns users against keeping an unencrypted digital copy of the secret key in photographs, files, emails or similar locations. This is especially important because there are actually two potential security problems. The first is compromising the wallet application and its locally protected secrets. The second is much simpler. An attacker compromises the phone and discovers that the owner has photographed the recovery phrase, saved it in Notes, emailed it to himself, stored it as a PDF or copied private keys into another application. At that point the attacker does not necessarily need to defeat the cryptographic protection of Exodus itself. The user has created another copy of the master secret somewhere else on the device. Exodus specifically warns that copying a private key places it on the device clipboard and recommends extreme caution when doing so. It also recommends keeping the 12-word secret key offline. There is another misconception worth correcting. Face ID does not magically make private keys immune to a sufficiently powerful operating-system compromise. Face ID, the Exodus lock and the iPhone passcode are extremely valuable security controls, particularly against unauthorized physical access. But a sophisticated kernel-level compromise belongs to a fundamentally different threat model. This is also why hardware wallets remain relevant. With Exodus Mobile alone, the wallet secrets ultimately exist on the general-purpose device that is also running Safari, messaging applications, email and thousands of other components. With a properly implemented hardware wallet, transaction signing and the critical private key material are isolated on dedicated hardware. Exodus itself recommends considering hardware wallets for significant holdings. That does not make hardware wallets invulnerable. A compromised iPhone could still manipulate what the user sees, attempt phishing, substitute addresses or trick the user into authorizing something malicious. The point is that extracting a hardware-protected private key is a very different problem from compromising a general-purpose smartphone containing a software wallet. There is also an important correction to the claims circulating about . The technically documented DarkSword research does not establish that range. Google documents DarkSword supporting iOS 18.4 through iOS 18.7. Lookout describes observed targeting approximately covering iOS 18.4 through iOS 18.6.2. Therefore I would not tell Exodus users that there is currently a publicly demonstrated exploit capable of stealing their wallet from every iPhone between iOS 13 and iOS 26.5. That is a substantially stronger claim than the evidence supports. What the research demonstrate is arguably important enough without exaggeration For Exodus users specifically, I think the most important lesson is not that Exodus itself has suddenly become insecure. That distinction is fundamental. You can build an excellent vault, but if somebody compromises the building containing the vault, you have to start thinking about a completely different security model. For meaningful amounts of cryptocurrency, I would therefore treat the phone as a transaction interface rather than the only security boundary protecting the entire portfolio. Keep iOS fully updated, keep Exodus updated, never photograph the 12-word secret key, never store it in Notes, email or an ordinary cloud file, avoid copying private keys unnecessarily and keep the recovery phrase physically offline. Exodus gives essentially the same guidance regarding offline storage of the secret key. And for substantial long-term holdings, separating the signing keys from the everyday phone with dedicated hardware significantly changes the threat model. The biggest takeaway from DarkSword is therefore not that . There is no evidence presented here establishing that. The real takeaway is more uncomfortable and more technically interesting
Every wallet has a story. The swaps you made the protocols you used and the activity you built over time can tell a bigger picture. That is the interesting angle behind @zerufinance . Instead of treating everyone like they are starting from zero Zaps bring existing onchain
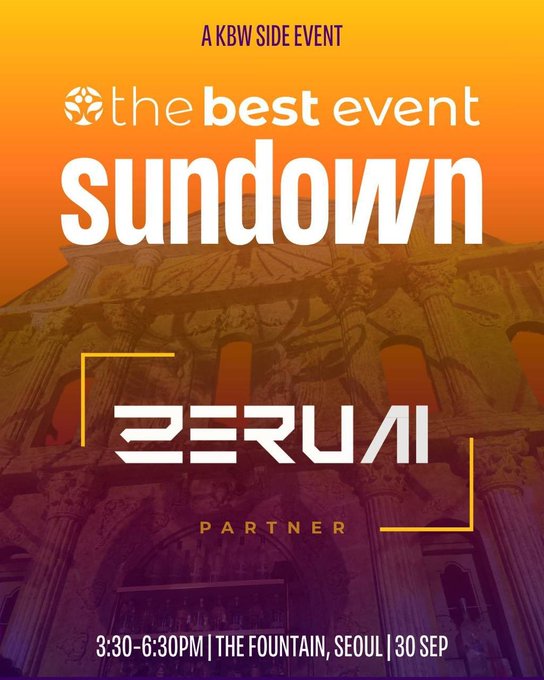
AI visual note: An event poster for "the best event sundown" featuring the text "ZERUN PARTNER" with event details "3:30-6:30PM | THE FOUNTAIN, SEOUL | 30 SEP".
Digital dollars become more useful when you can actually spend them. @cashi connects digital money to everyday payments, while letting you earn cashback along the way. Hold less. Use more. app.cashi.com/Ir0J/lumina
consistency gets a lot easier when you stop trying to solve your whole life at once
Join X Launch event, trade and win a share of 20,000,000 XDP! @doppler_fi @okx
good to see people sharing their stories, always interesting how perspectives change over time
gBeldex
token2049 by day and dj soda by night is a pretty solid combo
BREAKING: TRUMP SAYS, “YOU BETTER GO OUT AND BUY STOCKS NOW. THIS COUNTRY WILL BE LIKE A ROCKETSHIP.” BIG STATEMENT FOR MARKETS. #XRP
Escrowed USDC guarantees real payment before work starts.
又是一个买大盘的
Privacy gets blamed every time
AI agents can execute trades in seconds but execution alone doesn't prove an agent deserves access to capital. Now @agenticscredit is building credit infrastructure for agentic finance around a simple framework: Trade → Earn → Build → Qualify. Instead of relying purely on
AI visual note: A digital artwork featuring a sleek, metallic black swan with glowing green accents floating on water, set against a dark cityscape with neon green lights and vertical white bars.